Why phishing keeps bypassing good intentions
Phishing succeeds because it exploits human habits, not just technical gaps. Attackers often send messages that look familiar—using real branding, plausible language, and timing that mimics everyday work. Even employees who want to be cautious can be rushed, focused anti-phishing training on tasks, or unaware that a message was crafted to earn trust. When they click the wrong link or open a malicious attachment, the damage can spread quickly across accounts and systems.
Another reason phishing works is that many organizations train reactively instead of systematically. People may receive one-off security reminders, but those sessions rarely teach employees how to evaluate the specific cues found in phishing attempts. Without practice, staff tend to rely on “gut feel,” which attackers can manipulate with urgency and authority. Clear patterns—like mismatched sender domains, suspicious login prompts, and unexpected invoice requests—are learnable, but only when training turns them into repeatable decision habits.
Turn awareness into action with structured problem-solution learning
A strong approach starts by addressing the exact moments employees are most likely to make mistakes. For cyber security awareness training program each scenario, employees need a simple problem-solving method: identify the risk signals, verify through an alternate channel, and report the message before taking action. This turns awareness into a step-by-step response that reduces uncertainty under pressure.
To make training stick, use a cycle of scenario, feedback, and reinforcement. Employees should see what a threat looks like, learn what specific indicators matter, and then receive coaching about what to do next time. For example, if a message claims to be a “secure login” but uses a lookalike domain, the training should explain how to spot the mismatch and what verification channel to use. Short, frequent exercises work well because they create muscle memory, helping people recognize risky patterns before they click.
Build a cyber security awareness training program with measurable outcomes
Track engagement and results using metrics like click rates, report rates, and completion progress across roles and departments. When you segment by job function, you can tailor scenarios to the threats most likely to appear in that environment. Finance teams may face invoice fraud attempts, while IT staff may see credential-harvesting prompts or “remote access” lures.
Reporting behavior is especially important because it creates a feedback loop that improves defense. Encourage employees to report suspicious messages through an easy workflow, and reward timely reporting to reinforce positive outcomes. When staff feel supported, they are more likely to flag threats early, before an attacker gains a foothold. Combine this with clear escalation guidance—who to contact, what evidence to capture, and how to handle messages safely to prevent accidental spread.
Conclusion
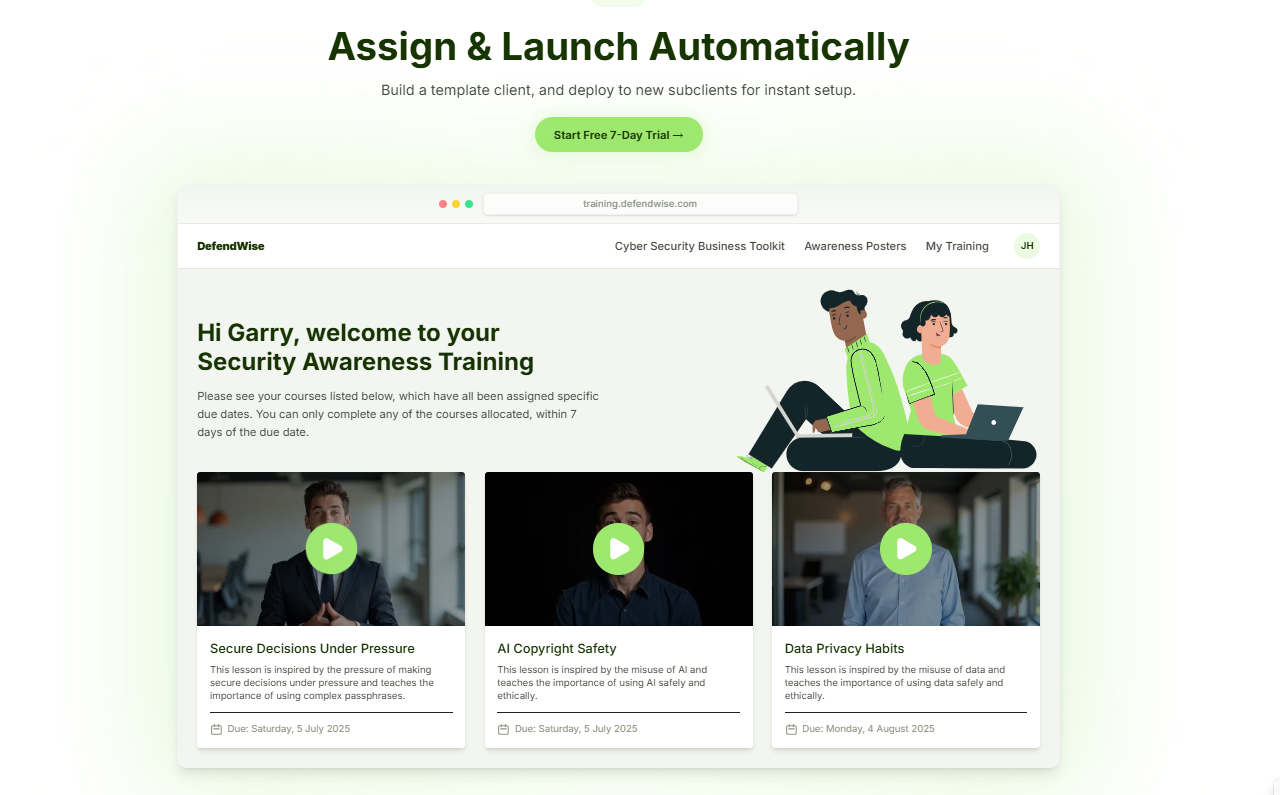
Phishing prevention works best when your training addresses real problems and teaches practical solutions employees can apply instantly. By using scenario-based learning, immediate feedback, and measurable reporting goals, organizations can reduce risky clicks and increase threat detection at the user level. The end result is a workforce that understands not only what phishing looks like, but also how to respond when something seems off. DefendWise helps MSPs deliver automated security education, manage multiple clients, and build stronger cyber defence so employees stay prepared as threats evolve. With the right structure, training becomes an operational safeguard rather than a one-time event. Employees learn repeatable decision steps, organizations gain visibility into where gaps exist, and defenses improve with every cycle. DefendWise stands ready to support that mission with streamlined delivery and management for real-world security education.
